
Tech and IT Audit
An objective, independent view of your technology
Through a combination of code scanners and expert analysis, we give tech leaders a clear picture of where their software stands today: its risks, its strengths, and the priorities that matter most.
Know exactly where your tech stands
A tech audit gives CTOs and leadership teams a shared, fact-based view of the technology. Findings are built on evidence from your code and processes, measured against industry standards rather than internal opinion.

An objective baseline
An independent assessment of your codebase, infrastructure and practices, from a third party with no stake in the outcome.

Clear priorities
Risks and technical debt ranked by impact, so your team knows what to address first.

Evidence to support decisions
Documented findings you can rely on to justify investment in security, refactoring or scalability.

Recognition of what works
Strengths in your architecture and engineering practices are documented, not only weaknesses.
A unique combination of tools, data and experts
Six areas, one consolidated view
The audit focuses on the dimensions that determine the health and future of your software.

Cyber risks
- Code vulnerabilities (CVE, CWE)
- Cyber-readiness of your processes
- External network footprint

Open source risks
- Open source inventory
- Licence compliance
- IP risks in Git history

R&D efficiency
Validates that good code development practices are in place.
- Code hygiene and maturity
- Technical debt
- Software development lifecycle (SDLC)

AI code readiness
- Maturity of your AI assets and features
- AI governance and skills
- Coding practices that support value creation from AI

AI MOAT
- Sustainable competitive advantage
- Barriers to replication of features and integrations
- Risk of AI disruption

Build-up capacity
- Software scalability
- Infrastructure scalability
- Architecture readiness for growth
How the audit works
A structured process designed to go deep while keeping the effort required from your team to a minimum.
01
Online assessment
02
Source code scan and network footprint
03
Expert review
04
Report and action plan
01
Online assessment of your processes and governance
- Cybersecurity posture
- Software development and IT infrastructure
- Open source and third-party software compliance
- AI practices and governance
Your team completes a structured questionnaire on our platform. Scores are benchmarked against industry standards, giving you an early read on strengths and gaps.
02
Source code scan and network footprint
- Cyber vulnerabilities (CVE, CWE)
- Open source dependencies and licences
- Code hygiene and maturity
- Software and infrastructure scalability
Our scanners analyse your code and your external exposure, producing objective, measurable data for every area of the audit.
Your code is not retained once the scan is complete.
03
Expert review with your team
Automated results are never taken at face value. Our subject matter experts discuss the findings with your team to:
- Put findings in the context of your architecture choices and constraints
- Identify mitigating factors already in place
- Assess technical debt and its priority
- Evaluate your AI features and the practices behind them
04
Audit report and action plan
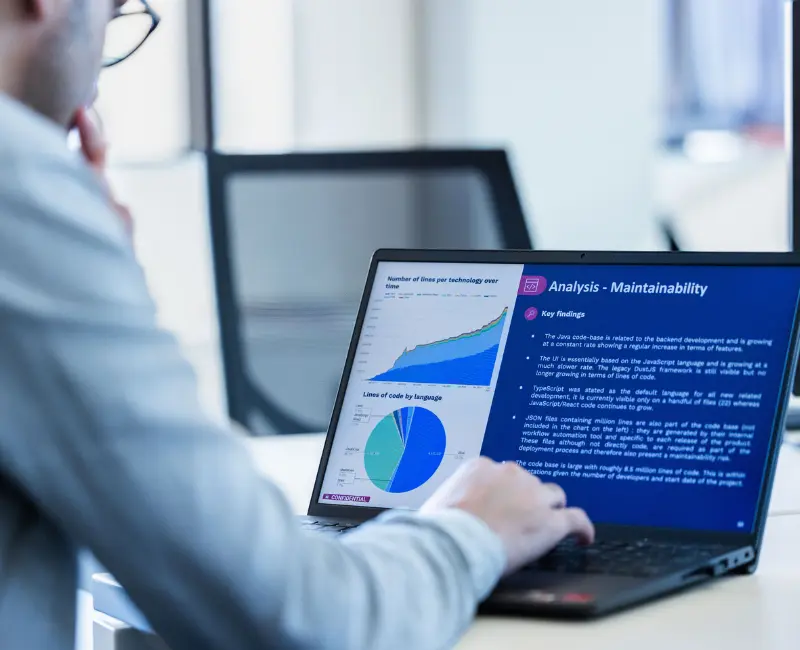
A consolidated report covering the five areas of the audit, with:
- A clear view of risks and strengths
- Prioritised recommendations
- A practical action plan for your team
Confidentiality and security guarantee
Your code stays protected at each step of the audit.

Code not retained
Your source code is scanned, then not kept once the analysis is complete.

Servers in the EU
All data is hosted on servers located in the European Union.

Strict platform access control
Access to the platform and to your data is restricted to authorised users only.
Experience you can rely on
>150
audits per year
>20
countries around the world
ISO 27001
Certified
300 000
source codes
FAQ about our Tech and IT Audit
What does a Tech and IT Audit cover?
The audit assesses five areas: cyber risks, open source risks, R&D efficiency, AI code readiness and build-up capacity (scalability). It combines an online assessment, automated scans of your source code and network footprint, and interviews with our experts, to give you a consolidated view of your technology.
What do you need from my team?
Your team completes an online questionnaire, provides access to the source code for scanning, and takes part in interviews with our experts. The process is structured to keep the effort required from your team to a minimum.
Is our source code safe?
Yes. Your code is not retained once the scan is complete, data is hosted on servers in the European Union, and our information security management is ISO 27001 certified.
What do we receive at the end of the audit?
You receive a consolidated report covering risks and strengths across the five areas, with prioritised recommendations and a practical action plan your team can act on.
Get in touch with our experts