Key points to remember:
- Equipment exposed to the internet can become entry points for cyberattacks, with significant consequences for a company’s operations and finances.
- Cyberattacks do not always require sophisticated techniques: out-of-date software or poorly secured systems can be enough.
- OSINT enables the remote identification of potentially vulnerable devices using publicly available information.
- Network Footprint analysis enables a company’s attack surface to be mapped and the cyber risks to which it may be exposed to be identified.
- For investors, incorporating the Network Footprint into tech due diligence enables them to verify a company’s actual exposure and anticipate the risks and security costs following an acquisition.
Danfoss cyberattack: what happened?
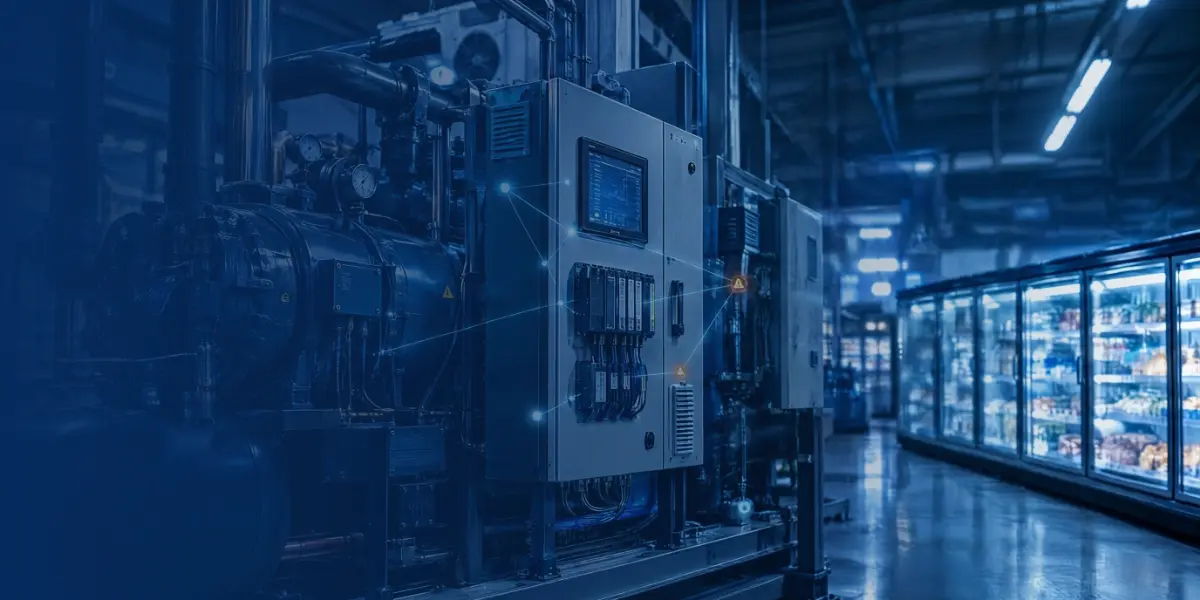
During the night of 11–12 October 2026, several major French retail chains were hit by a cyberattack targeting their refrigeration control systems. The attackers succeeded in remotely altering certain temperature settings, disrupting the operation of the refrigeration systems and resulting in the destruction of goods. (Associated Press, 13 October 2026) [1]
A few months earlier, cybersecurity researchers at Claroty had identified several vulnerabilities affecting Danfoss AK-SM 800A refrigeration controllers. Their research had also revealed 2,765 management interfaces accessible via the internet, according to data from the Censys platform. (Claroty, 9 August 2026) [2]
Interview: analysis by our cybersecurity expert
1. In your view, what is the main lesson to be learnt from the cyberattack involving Danfoss equipment in terms of cybersecurity?
Above all, this attack shows that it is not necessary to deploy extremely sophisticated methods to cause considerable damage. Equipment exposed to the internet, known vulnerabilities and unapplied updates can be enough to compromise an entire infrastructure. What stands out here is how a simple point of entry can lead to serious operational and financial consequences.
This is precisely why visibility into one’s network footprint is essential: you cannot properly protect what you do not know exists or is accessible.
2. How were the attackers able to identify vulnerable devices exposed to the internet?
This is precisely what makes OSINT (Open Source Intelligence) so valuable, but it is also where the risk lies. Today, search engines such as Shodan and Censys make it possible to identify devices connected to the internet based on their technical specifications, exposed services or signatures specific to certain manufacturers. In the case of Danfoss, researchers at Claroty had already demonstrated that it was possible to find thousands of publicly accessible administration interfaces. We do not yet know precisely what method the attackers used, but this type of reconnaissance can be largely automated. What would take weeks to search for manually can now be identified on a large scale in a matter of minutes.
3. What might a Network Footprint analysis have revealed before this attack?
Potentially a great deal. A Network Footprint analysis enables the mapping of assets accessible via the internet, the identification of exposed services and the technologies used, and, where possible, their versions and associated vulnerabilities. In this specific case, it could, in particular, have highlighted the presence of industrial control interfaces directly accessible via the internet, which in itself constitutes a significant warning sign. This is what we do regularly at Vaultinum: observe a company from the outside, with a level of visibility similar to that which an attacker might have, in order to identify points of exposure that warrant investigation or remediation. Obviously, this is no substitute for a penetration test or an internal audit, but it is an extremely useful first step in detecting risks that are sometimes overlooked by the company itself.
4. What are the major security risks you most frequently identify during a Network Footprint analysis?
The most common issues are unnecessarily exposed administration services, obsolete software or components, known unpatched vulnerabilities, and test or development environments that are publicly accessible. We also quite regularly come across configuration errors, exposed sensitive information, or forgotten systems that continue to operate without proper monitoring. The problem is not always a particularly critical vulnerability taken in isolation. It is often the accumulation of minor oversights – sometimes in combination with one another – that ultimately creates a genuine risk. Above all, these exposures are not necessarily known to internal teams, particularly when the infrastructure has evolved rapidly or relies on multiple service providers.
5. What lessons should private equity funds learn from this attack to better assess cyber risks during a tech due diligence process?
I believe this incident serves as a reminder that a cybersecurity posture cannot be assessed solely through questionnaires, internal policies or certifications. A company may have a structured governance framework and yet still have significant points of exposure on the internet of which it is not necessarily aware. For an investor, the value of the Network Footprint lies precisely in cross-checking the company’s statements against independent, factual technical observations. This helps to identify risks that could lead to remediation costs, business disruptions or financial consequences following an acquisition.
The aim is not to look for vulnerabilities in order to devalue a company, but to give investors a more objective view of its actual exposure and any investments that may be required to secure it.
Greater visibility into cyber risks prior to acquisition
The cyberattack involving Danfoss equipment serves as a reminder that security vulnerabilities are not limited to traditional IT systems. Connected devices, exposed services and inadequately secured infrastructure can also pose operational and financial risks to businesses.
For private equity investors, the Network Footprint analysis complements the cybersecurity assessment carried out during technology due diligence. By providing an independent view of a target company’s external exposure, it helps to identify risks requiring further investigation and to anticipate any remediation investments that may be needed.
This approach thus helps investors to incorporate cyber risks into their assessment of the technology assets and into their post-acquisition security priorities.
Disclaimer
The opinions, presentations, figures and estimates set forth on the website including in the blog are for informational purposes only and should not be construed as legal advice. For legal advice you should contact a legal professional in your jurisdiction.
The use of any content on this website, including in this blog, for any commercial purposes, including resale, is prohibited, unless permission is first obtained from Vaultinum. Request for permission should state the purpose and the extent of the reproduction. For non-commercial purposes, all material in this publication may be freely quoted or reprinted, but acknowledgement is required, together with a link to this website.
Sources
- Associated Press, 13 October 2026 — apnews.com
- Claroty Team82, 9 August 2026 — blog.claroty.com